Non classé
Oil and Gas Carbon, Methane, and Product Traceability: A Supply Chain Imperative

Published
4 mois agoon
By
Carbon and methane management are no longer isolated sustainability reporting topics. They are becoming core supply chain requirements that influence product acceptance, customer contracts, financing, regulatory exposure, and access to premium markets. For oil and gas companies, the strategic question is shifting from whether emissions are reported to whether emissions can be traced credibly across assets, movements, products, and customers.
Oil and Gas in the Supply Chain: A Strategic Framework for Building Resilient and Responsible Supply Chains.
This is a significant operating change. Traditional emissions reporting was often annual, aggregated, and functionally separated from day-to-day supply chain execution. Product traceability requires a different model. It connects emissions data to physical flows, commercial claims, and operational decisions. It asks whether a company can demonstrate where a product originated, which assets handled it, how it was processed and transported, what methane evidence supports the claim, how carbon intensity was calculated, and whether the data can withstand customer, regulator, or third-party audit scrutiny.
In that sense, emissions traceability is becoming a supply chain discipline. It requires the same rigor that companies apply to custody transfer, quality specifications, inventory control, logistics execution, and contract compliance.
Why Product Traceability Matters
Oil and gas products are increasingly differentiated by emissions profile. Buyers may be seeking lower-methane natural gas, lower-carbon LNG, responsibly sourced crude, verified low-carbon industrial fuels, or feedstocks with documented carbon intensity. These claims cannot rest on broad corporate averages alone. They require a defensible chain of data that links physical product flows to specific emissions sources and calculation methods.
This is particularly important because energy supply chains are complex. A barrel, molecule, or cargo may pass through production sites, gathering systems, processing facilities, pipelines, storage terminals, liquefaction assets, marine transport, refineries, distribution networks, and end customers. Each step can introduce emissions, data gaps, allocation challenges, or contractual ambiguity.
As customers become more sophisticated, they will ask more practical questions. Where did the product originate? Which assets touched it? Were methane leaks measured or estimated? How were flaring and venting accounted for? What emissions factors were used? Was purchased power included? How were shared assets allocated? Can the claim be verified? Companies that can answer these questions consistently will be in a stronger position than companies relying on broad statements of intent.
Scope 1, Scope 2, and Scope 3: The Supply Chain View
Oil and gas companies must manage emissions across all three scopes, but the supply chain implications differ.
Scope 1 emissions are direct emissions from owned or controlled operations. In oil and gas, this includes combustion, flaring, venting, methane leakage, process emissions, and company-operated vehicles and equipment.
Scope 2 emissions are indirect emissions from purchased electricity, steam, heat, or cooling. These emissions can vary meaningfully depending on the power source and the location of the asset.
Scope 3 emissions are indirect value chain emissions. For oil and gas, this may include purchased goods and services, transportation, refining, distribution, product use, and end-customer combustion.
Scope 3 is especially challenging because it is large, complex, and often debated. Different stakeholders may interpret responsibility and materiality differently. However, methodological disagreement does not eliminate the need for clarity. Customers, investors, regulators, and business partners increasingly expect companies to explain what is included, what is excluded, how calculations are performed, and how methods are applied over time.
The supply chain lesson is straightforward: credibility depends on consistency and transparency. A company does not need to resolve every industry debate unilaterally, but it does need governance, documentation, and repeatable methods that can be explained and audited.
Methane Visibility Is Moving from Estimate to Measurement
Methane is one of the most important emissions issues for the oil and gas sector. It is material, increasingly regulated, and often addressable through operational improvements. The industry is moving from estimated methane toward measured methane, and that shift has major implications for operations, maintenance, and supply chain claims.
Measurement technologies include continuous monitoring sensors, satellite detection, aerial surveys, optical gas imaging, drone-based inspections, mobile monitoring, leak detection and repair programs, compressor and valve monitoring, and flaring and venting data capture. These tools are valuable, but technology alone is not enough. The real value comes when detection is integrated into maintenance planning, work management, operational response, compliance reporting, and commercial documentation.
A methane alert that does not generate a timely investigation or repair has limited operational value. A measurement program that cannot be reconciled with asset data, production data, and product claims has limited commercial value. Methane management must become an operating discipline, not a disconnected reporting exercise.
Product-Level Carbon Intensity Becomes a Market Capability
Product-level carbon intensity connects emissions to specific products, shipments, cargoes, or customers. This capability is becoming increasingly relevant for crude grades, natural gas, LNG cargoes, refined products, petrochemical feedstocks, hydrogen, natural gas liquids, and industrial fuels.
The challenge is allocation. Companies must determine how emissions are assigned across production, processing, transportation, storage, refining, and distribution. Shared infrastructure complicates the process. So do commingled flows, changing operating conditions, and multiple product outputs from the same facility. Nevertheless, customer and regulatory expectations are moving toward more granular claims.
Companies that can provide credible product-level data will have more options. They may be better positioned to serve customers with emissions-related procurement requirements, support differentiated product offerings, participate in emerging certification schemes, and defend commercial claims. The advantage is not simply reputational. It can affect market access and contract competitiveness.
The Role of Digital Carbon Ledgers
A digital carbon ledger is a system of record for emissions-related events and calculations. At a minimum, it should capture the source, timestamp, quantity, emissions factor, methodology, asset or process association, product linkage, and verification status. The goal is not to create another static reporting database. The goal is to create confidence in the claims a company makes.
A strong carbon ledger can support audit readiness, customer reporting, regulatory compliance, internal carbon pricing, methane reduction tracking, supplier accountability, product differentiation, and carbon intensity certification. It can also help reconcile differences between operational data, sustainability reporting, and commercial documentation.
This is particularly important in an environment where greenwashing concerns are high and scrutiny is increasing. Claims about lower-carbon products, methane performance, or responsibly sourced energy must be supported by data lineage. Leaders should ask whether the company can trace a number back to the source system, the asset, the calculation method, and the approval workflow. If not, the claim may be difficult to defend.
Carbon Is Entering the Contracting Process
Carbon and methane data are increasingly becoming part of commercial agreements. Supply chain contracts may include reporting obligations, data-sharing requirements, verification standards, carbon intensity thresholds, methane performance clauses, audit rights, offset treatment, and allocation of credits or claims.
This changes the nature of supply chain contracting. Procurement, legal, commercial, operations, sustainability, and technology teams must work together. Carbon language that is written without operational input can create risk. For example, a contract may require data that current systems cannot provide, verification that current workflows do not support, or performance commitments that are not aligned with maintenance and asset integrity realities.
Commercial teams also need clarity on ownership of claims. If emissions reductions are achieved in a shared supply chain, who can claim them? If offsets are used, how are they treated? If a customer requires product-level carbon intensity, what verification standard applies? These questions are increasingly commercial, not just environmental.
ESG Credibility Depends on Operational Proof
ESG credibility in oil and gas depends on evidence. Methane reduction, flaring reduction, water stewardship, spill prevention, contractor safety, community impact, supplier governance, and transparent reporting all have operational and supply chain dimensions. The strongest ESG programs are embedded in how assets are run, how suppliers are managed, how products move, and how data is governed.
This requires clear metrics, defined accountabilities, consistent methodologies, and verified data. It also requires avoiding the separation of ESG from the business. When sustainability claims sit outside operational systems, they are more vulnerable to inconsistency and challenge. When they are connected to asset performance, maintenance actions, logistics flows, and customer commitments, they become more credible and more useful.
Accountability as Competitive Advantage
The oil and gas companies that build credible emissions traceability will have an advantage. Not because they can claim perfection, but because they can demonstrate control, transparency, and improvement. Customers, investors, regulators, and communities may accept a realistic transition path. They are less likely to accept vague claims, inconsistent methods, or weak measurement.
For executives, the practical path forward begins with a few questions. Which emissions claims are already being made to customers and investors? Which products or customers require more granular data? Where are the largest methane data gaps? Can emissions data be tied to assets, flows, and shipments? Are contract commitments aligned with operational capabilities? Is there a governed ledger that can support audit and verification?
Carbon and methane traceability is not just a compliance burden. It is becoming part of the operating model for energy supply chains. Companies that treat it as a supply chain capability will be better prepared for changing customer expectations, regulatory requirements, and market differentiation.
To explore these issues in more depth, Download the full ARC Advisory Group white paper on oil and gas supply chain transformation.
Download Oil and Gas in the Supply Chain.
The post Oil and Gas Carbon, Methane, and Product Traceability: A Supply Chain Imperative appeared first on Logistics Viewpoints.
You may like
Non classé
Octave Puts Trusted Industrial Data at the Center of OT Cybersecurity
Published
10 heures agoon
4 novembre 2026By
Octave is revamping its cybersecurity and operational technology software portfolio with a broader platform strategy emphasizing trusted industrial data, operational resilience, and ecosystem integration. A key component of this strategy is Octave Cyber Integrity, which addresses the need for accurate, detailed, and continuously updated information regarding assets, configurations, vulnerabilities, and changes across diverse control system environments in the world of OT.
Octave is positioning Cyber Integrity as a reliable foundation for OT cybersecurity by integrating deep configuration-based asset identification with broader industrial data sources. This approach signifies an intensified commitment and acceleration of capabilities to provide the market with continuously maintained, accurate cybersecurity data, which is critical for operational resilience, risk prioritization, ecosystem collaboration, and AI-enabled decision-making.
Octave takes a different approach from traditional OT asset discovery models that mainly rely on passive network monitoring or active scanning. The company emphasizes configuration-based visibility using backups and control system data to create a comprehensive representation of industrial assets, including devices from Level 0 to Level 3.5, as well as firmware, software, I/O, control strategies, patch status, and configuration baselines. This method is well-suited for critical infrastructure environments where active interrogation of control assets could introduce operational risks.
Octave’s new platform direction means that cybersecurity data is now being integrated into the industrial data layer rather than existing as a separate security dataset. By providing access to Cyber Integrity data through an intelligent layer, and eventually through APIs for third-party security and other cybersecurity vendors, Octave is establishing asset integrity and data integrity as essential for AI-enabled operations, more effective cyber risk management, and collaborative OT cybersecurity initiatives. With this approach to data, the company is also laying the foundation for the creation of a cybersecurity digital twin.
Octave Is Reframing Industrial Software Around Trusted Data
Octave is an independent software and SaaS company that emerged from Hexagon’s planned separation of several software businesses, including Hexagon’s Asset Lifecycle Intelligence and Safety and Infrastructure & Geospatial divisions, along with ETQ, Bricsys, and Projectmates. Hexagon announced the Octave name in 2025 as the identity for the spin-off, and the company completed its separation in mid-2026. Octave now operates as a standalone public company (Nasdaq: OCTV) focused on mission-critical software for industrial and public-sector organizations.
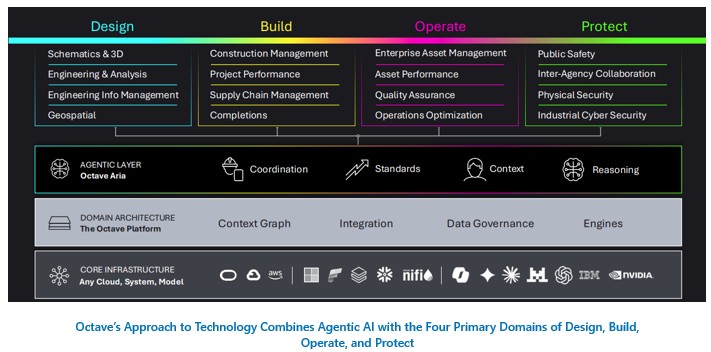
The company inherits a broad portfolio built around the lifecycle of physical assets. Its new approach spans four workflow environments: design, build, operate, and protect. This heritage means that Octave does not approach cybersecurity as a standalone discipline. It connects cybersecurity to engineering data, operations, asset lifecycle management, public safety, physical security, and quality workflows.
Octave positions itself as a differentiated industrial software company by combining engineering, operations, safety, cybersecurity, and physical security capabilities around an AI-ready industrial data fabric and continuous digital thread. Its strategy emphasizes open, contextualized data, SaaS delivery, and human-guided industrial AI to help asset-intensive organizations improve lifecycle efficiency, resilience, and operational decision-making.
Octave’s New Business Approach: A Common Foundation of Contextual Data
Octave’s new business approach moves the company beyond a product-centric model toward a platform and ecosystem model. Instead of treating OT cybersecurity, physical security, engineering data, and operational intelligence as isolated domains, Octave emphasizes a common foundation of contextualized industrial data. This approach aligns with the requirements of asset-intensive industries that must manage security, reliability, safety, compliance, and operational performance across complex multi-site operations.
This strategy matters most in industries such as oil and gas, power, chemicals, and utilities, where valuable cybersecurity insights often depend on engineering context and configuration detail that traditional IT security tools do not capture. Octave recognizes that no single vendor or detection method can fully address OT cybersecurity on its own. Effective programs require accurate asset intelligence, configuration integrity, operational context, and mechanisms to share trusted data with adjacent tools and workflows.
The Octave Platform: Building an Industrial Data Layer
The Octave platform strategy centers on a unified, trusted data layer that supports design, build, operate, and protect workflows. Cybersecurity data, especially asset inventory and configuration information, becomes a key input to this intelligence layer. In this model, OT cybersecurity extends beyond threat detection. It also requires a reliable representation of the industrial environment so security, operations, and engineering teams can act from a shared source of truth.
This platform direction matters because many OT risk programs still operate with fragmented asset data. Passive discovery tools identify network-connected devices, vulnerability tools maintain separate patch records, engineering systems hold configuration data, and compliance teams track controls in separate processes. Octave seeks to consolidate these data domains so organizations can use asset identity, configuration state, vulnerability exposure, backup status, and operational context together for faster and more effective remediation and mitigation of OT cybersecurity risk.
Octave Cyber Integrity and the Role of Deep Asset Identification
Cyber Integrity sits within Octave’s Protect portfolio. The product has its roots in PAS Cyber Integrity, which Hexagon previously offered through its Asset Lifecycle Intelligence business. As part of Octave, Cyber Integrity can now support a solution-level approach that combines deep OT asset and configuration data with lifecycle intelligence, operational context, and domain-specific AI. Octave Cyber Integrity identifies, evaluates, and prioritizes OT/ICS cybersecurity risk by capturing critical asset, vulnerability, and configuration data. This elevates the role of Cyber Integrity to that of a risk management and resilience platform for multi-vendor industrial control system environments.
Octave’s value proposition depends on the distinction between basic asset discovery and deep asset identification. Passive IDS-based discovery provides useful network visibility, including IP addresses, MAC addresses, and traffic relationships. However, passive discovery alone often lacks the depth required to validate control system configurations, identify firmware and software detail, understand patch posture, or maintain a known-good baseline. Active scanning adds detail, but in sensitive OT environments it can raise concerns about device stability, vendor warranty exposure, and operational disruption.
Cyber Integrity addresses this gap with a configuration-based approach. It collects backups and control system configuration data to build a more detailed inventory without directly interrogating live control assets in ways that could affect operations. This method requires more time and engineering effort than passive packet capture, but it provides richer data for vulnerability assessment, configuration change detection, compliance, recovery, and lifecycle planning.
Asset Integrity, Data Integrity, and OT Cybersecurity
Cyber Integrity links asset identification with data integrity by establishing a trusted representation of what exists in the control environment, how each asset is configured, whether that configuration has changed, and how those changes affect cyber risk and operational resilience. In OT environments, inaccurate data can lead to missed vulnerabilities, poor remediation priorities, failed audits, delayed recovery, and unnecessary operational disruption.
Deep configuration data also improves vulnerability management. Rather than relying only on generic device identification or network observations, organizations can correlate asset attributes, patch levels, firmware, installed software, system criticality, and configuration state. This context gives teams a stronger basis for determining whether a vulnerability applies, whether remediation is technically feasible, and which actions deserve priority based on operational impact.
Data integrity becomes all-important as industrial organizations apply AI and advanced analytics to OT cybersecurity and operations. AI models depend on the quality, completeness, and trustworthiness of the data they consume. By feeding verified asset and configuration data into a common intelligent layer, Octave positions Cyber Integrity as an enabler of more reliable analytics, decision support, threat detection, and remediation workflows.
Ecosystem and API Strategy
Octave also plans to expose deep asset inventory data through APIs for integration with third party cybersecurity vendors. Most end users rely on multiple tools, including passive monitoring, threat detection, vulnerability management, SIEM, and service management platforms. No single vendor owns the full workflow. By opening Cyber Integrity data to partners, Octave can allow products from vendors such as Dragos, Nozomi Networks, and Claroty to use a deeper asset and configuration foundation, subject to partner agreements and customer approvals. This approach strengthens the broader OT cybersecurity ecosystem by improving data quality across detection, vulnerability prioritization, incident response, and compliance workflows.
Recent Attacks on US Water Infrastructure Show the Importance of Good OT Asset and Configuration Data
Recent attacks on U.S. water and wastewater infrastructure underscore why trusted OT asset and configuration data have become operationally critical. Federal agencies have warned that malicious actors are targeting internet-facing programmable logic controllers, including Rockwell Automation/Allen-Bradley MicroLogix controllers, changing IP addresses and passwords, modifying project files, and causing operational effects such as loss of monitoring, loss of control, pressure loss, flooding, boil-water notices, and sustained manual operations. Earlier campaigns against PLCs in the water sector showed a similar pattern: exposed control devices, weak or default credentials, and limited visibility into controller configurations created opportunities for attackers to disrupt or deface operational systems.
Octave Cyber Integrity is relevant to these incidents because it focuses on the underlying weaknesses that made them possible. Incomplete OT inventories, undocumented internet exposure, weak configuration control, and limited ability to compare current controller state with trusted baselines are all major contributors to the likelihood of a serious cyber incident. By maintaining detailed asset identity, firmware, software, configuration, backup, vulnerability, and change data, Cyber Integrity can help water utilities identify exposed or misconfigured PLCs, validate whether unauthorized changes have occurred, prioritize remediation based on operational criticality, and restore systems from known-good backups. In this context, Cyber Integrity becomes more than an inventory exercise; it becomes a practical foundation for resilience in water infrastructure where operators must preserve safe service even when control systems are targeted.
Creating a Cybersecurity Digital Twin
Cyber Integrity data and the Octave platform have the potential to combine to create a cybersecurity digital twin. In this model, Cyber Integrity would provide the detailed technical foundation: asset identity, firmware, software, configuration files, control logic, backup status, patch levels, vulnerability exposure, and change history. The Octave platform would add lifecycle context, operational relationships, engineering data, workflow status, and domain-specific intelligence. Together, these data sets could create a continuously maintained digital representation of the OT cyber-physical environment.
Cybersecurity digital twins differ from traditional engineering digital twins because they focus on cyber risk, configuration integrity, and operational resilience. A cybersecurity digital twin can show which assets exist, how they connect to processes and systems, what known-good configurations look like, where vulnerabilities apply, which changes deviate from approved baselines, and how a cyber event or remediation action could affect operations. Security, engineering, and operations teams could use this shared model to evaluate cyber risk before taking action in the live environment.
The concept could also improve incident response and recovery. If an organization maintains a current cyber twin, it can compare the live environment with trusted baselines, identify unauthorized changes, assess the operational importance of affected assets, and prioritize restoration from validated backups. This would move cyber recovery from a largely reactive process toward a more structured, model-driven workflow that links cybersecurity decisions to process criticality and asset lifecycle data.
Over time, a cybersecurity digital twin could become a foundation for AI-assisted risk analysis. Octave could use verified Cyber Integrity data and broader platform context to help teams simulate attack paths, evaluate remediation options, identify high-risk configuration drift, and recommend actions based on both cyber exposure and operational impact. The value of this model would depend on data quality, governance, integration with partner tools, and the customer’s ability to keep the twin synchronized with the real OT environment.
Conclusions & Recommendations
Octave’s approach reflects an important industry trend: effective OT cybersecurity increasingly depends on the integrity of the underlying industrial data. Cyber Integrity is more than a simple OT asset inventory product. It serves as a source of trusted industrial cybersecurity data that supports risk management, resilience, compliance, and AI-enabled decision-making across the broader Octave platform. By capturing backups and configuration data, Cyber Integrity helps organizations build a more complete understanding of assets, vulnerabilities, baselines, and unauthorized change. Octave’s planned API and ecosystem strategy could further increase the value of Cyber Integrity by allowing customers and partner tools to use deep asset data without duplicating collection efforts. In ARC’s view, Octave is well positioned to benefit from growing market demand for reliable OT asset intelligence and stronger integration between cybersecurity, operations, and engineering data.
End users should evaluate Octave’s approach against their OT cybersecurity maturity. Early-stage programs may begin with passive discovery to establish basic visibility. More mature programs, especially in critical infrastructure, will benefit from using deep configuration-based inventory to strengthen vulnerability management, change control, compliance, backup, recovery, and operational resilience.
Octave’s platform strategy also reinforces the need to treat OT cybersecurity as part of enterprise industrial data management. Asset inventory, configuration state, vulnerability posture, and recovery data should not remain isolated within specialized security tools. These data sets should inform engineering workflows, maintenance planning, modernization decisions, compliance reporting, and executive-level cyber risk governance.
The post Octave Puts Trusted Industrial Data at the Center of OT Cybersecurity appeared first on Logistics Viewpoints.
Non classé
The Systems-Engineered Logistics Operation: From Transformation Projects to Continuous Design
Published
2 jours agoon
3 novembre 2026By
For years, logistics transformation has been organized as a succession of projects. Implement the platform. Build the control tower. Automate the facility. Add the AI layer. The problem is that logistics no longer changes on a project cadence.
That environment is disappearing. The future logistics will need to be designed continuously. The Autonomous Logistics Network is one expression of this end state, but reaching it requires continuous design rather than a one-time transformation project.
Stop Thinking in Technology Stacks
Modern logistics networks are becoming integrated combinations of physical assets, software, data, optimization, AI, robotics, people, partners, and automated decisions. Calling this a technology stack understates what is happening.
It is an operating system. The important design questions are no longer confined to which applications a company owns. Leaders have to consider how decisions flow, how data maintain continuity across systems, how automation interacts with people, how models are governed, how exceptions escalate, and how the organization behaves when components fail.
That is systems engineering territory. The companies that manage this architecture deliberately will have an advantage over those that continue adding capabilities one project at a time.
Intelligence Is Moving to the Point of Action
Logistics technology is moving from systems of record toward systems of decision. Traditional applications captured transactions and supported workflows. Analytical systems added prediction and optimization. The emerging layer increasingly combines real-time signals, AI, optimization, agents, and execution connectivity.
The result is intelligence closer to the point of action. A shipment delay can be identified, its impact evaluated, alternatives generated, and a response executed with limited human intervention. Transportation systems can continuously re-evaluate routes, capacity, and exceptions instead of waiting for manual replanning. Warehouse and yard systems can adjust priorities as conditions change.
This will make logistics faster. It will also make architecture and governance more consequential.
When software only reported information, a bad output could be ignored. When software acts, the operating envelope matters.
Human Work Moves Up the Decision Stack
More automation does not eliminate the human role. It changes it.
People will spend less time collecting information, reconciling spreadsheets, monitoring routine transactions, and making repetitive bounded decisions. They will spend more time dealing with novel exceptions, cross-functional tradeoffs, strategic choices, carrier and customer relationships, system design, and governance.
That is a better use of human capability. It is also a harder job.
The future planner, transportation manager, warehouse leader, or logistics executive will need to understand not only operations but the automated systems influencing operations. They will need to know when to trust a recommendation, when to challenge it, and how a decision in one part of the system affects another. Logistics expertise will become more architectural.
Continuous Design Requires Continuous Validation
If the system changes continuously, validation must become continuous as well.
AI models drift. Business priorities change. automation rules evolve. New interfaces are added. Local process changes accumulate. External conditions move.
The organization cannot wait for the next transformation program to determine whether the operating system still meets its requirements. Performance, model behavior, exception patterns, overrides, decision latency, data quality, and failure modes will need ongoing monitoring.
This creates a closed lifecycle: design, deploy, observe, validate, improve, and redesign. Transformation becomes less of an event and more of a management discipline.
Resilience Becomes an Architectural Property
The future of resilience is also likely to move beyond static buffers. Inventory and redundancy will remain important, but digital systems will make logistics more capable of sensing, simulating, and responding dynamically.
A disruption can trigger scenario analysis. A digital twin can estimate consequences. Optimization can evaluate alternatives. AI can interpret unstructured signals. Automated decision systems can act inside approved boundaries.
This does not eliminate the need for physical resilience. It allows physical resilience and decision resilience to work together.
The strongest logistics networks will not simply carry more protection. They will understand their dependencies and reconfigure faster when conditions change.
Architecture Becomes a Competitive Capability
For years, companies differentiated logistics through network scale, facility and transportation assets, carrier leverage, operational excellence, service design, and technology investment. Architecture is becoming another source of advantage.
Two companies may use similar software and still achieve very different results because one has better process integration, clearer decision rights, stronger data, more effective automation boundaries, better failure recovery, and tighter governance. The advantage does not come from owning the component. It comes from how the components have been engineered to work together.
Logistics Management Becomes Systems Management
That may be the larger lesson of this series. Logistics networks are already systems of systems. The technology is making them more connected, more autonomous, and more adaptive. That complexity cannot be managed indefinitely through functional optimization and periodic implementation projects.
The discipline has to evolve.
Define requirements before selecting solutions. Design the operating model. Architect processes, data, and decisions together. Engineer technology into the system rather than around it. Validate the outcome. Govern change. Design for failure. Improve continuously.
The competitive advantage will not come from owning the same AI, automation, TMS, WMS, visibility, and execution technologies everybody else can buy. It will come from how coherently those components have been engineered to work together. The future of logistics management is not simply more digital, more autonomous, or more intelligent. It is more engineered.
Related Logistics Viewpoints research
Systems Engineering in Logistics
The New Architecture of Logistics
2026 Supply Chain Decision Intelligence Market Map
Digital Transformation in Logistics
Previous in this series: Design for Failure: Resilience, Risk, and Failure Modes
Request the Systems Engineering in Logistics Client Edition
If your organization is evaluating a logistics transformation, technology strategy, automation program, or operating-model redesign, I would be glad to provide the complete client edition and discuss how the framework applies to your priorities, constraints, and operating environment.
The post The Systems-Engineered Logistics Operation: From Transformation Projects to Continuous Design appeared first on Logistics Viewpoints.
Non classé
Walmart and Symbotic: When Warehouse Automation Becomes a Network Strategy
Published
2 jours agoon
3 novembre 2026By
Warehouse automation has traditionally been discussed one facility at a time. A retailer installs an automated storage system, deploys mobile robots, adds robotic picking, or upgrades sortation. The business case is then measured against improvements within that particular building. Walmart and Symbotic are beginning to challenge that way of thinking.
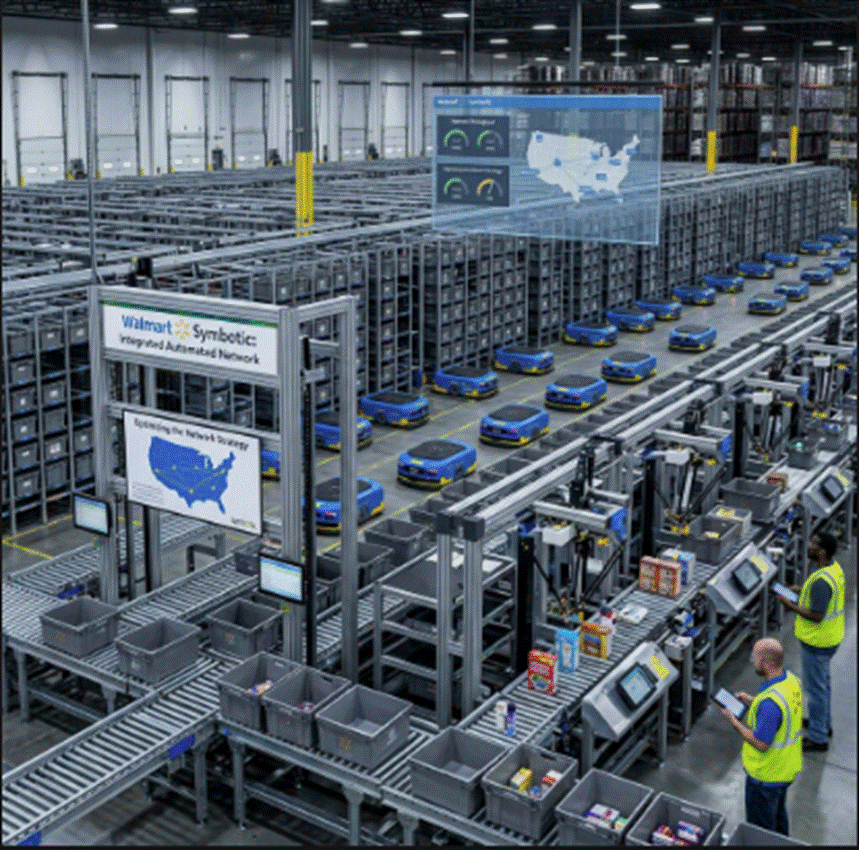
On October 29, Walmart and Symbotic announced an expanded commercial agreement that will bring additional automation capabilities to 25 U.S. regional distribution centers. The agreement includes an initial commitment of approximately $6 billion, covering work over several years and multiple locations. Walmart says the initiative is intended to support upstream e-commerce inventory management, increase storage capacity, and improve the movement of products through its supply chain. Those numbers make the announcement noteworthy. But the more interesting story is what the scale of the commitment says about the next phase of warehouse automation.
From an Automation Project to an Operating Model
For years, warehouse automation investments were frequently justified around specific bottlenecks: reduced picker travel, increase storage density, improve sortation throughput, or offset labor requirements. Those are still important objectives. But Walmart is evaluating automation against something larger: the performance of an interconnected distribution network supporting stores, pickup and home delivery.
Rob Montgomery, executive vice president for Walmart U.S. Supply Chain Operations, tied the expanded agreement to improving service, growing capacity, simplifying work for associates and lowering costs. The company also expects the expansion to support broader assortment, greater speed and more reliable replenishment. That distinction matters.
Warehouse automation increasingly needs to be evaluated not simply by asking, “How much faster can this facility pick?” but by asking, “What does this investment change across the supply chain?” Does additional storage capacity improve inventory positioning? Does automation enable later ordering cutoffs? Can replenishment become more predictable? Can the same technology architecture be repeated across multiple facilities without redesigning the operation every time? Those questions take warehouse automation discussions much closer to business strategy.
Scale Is Becoming Part of the Business Case
The Walmart-Symbotic relationship is particularly interesting because this is not a new pilot. Reuters reported that Symbotic has been helping automate Walmart’s supply chain since 2017, while the latest agreement extends automation to another 25 regional distribution centers. There is another layer to the expansion as well. Supply Chain Dive reported that Walmart committed an additional $125 million toward research and development of racking technology and related picking, process-flow and inventory-management capabilities. That is important because it suggests the competitive discussion is moving beyond individual pieces of robotic hardware. Warehouse automation is increasingly about how storage, picking, inventory, material movement and software operate together.
Symbotic’s current portfolio illustrates that evolution. The company says its integrated offering includes BreakPack for each-picking and SymMicro for e-commerce micro-fulfillment, supported by proprietary software that uses AI to orchestrate product movement. The question for warehouse operators, therefore, becomes less about which robot performs an individual task and more about how multiple automation layers combine into a repeatable operating system.
Walmart Is Not the Only Signal
Developments elsewhere reinforce the same trend. Amazon reported in 2026 that it has deployed more than one million robots across its operations network. Its systems now span inventory handling, mobile robotics, robotic arms and packaging automation. The company also says its Sequoia system can identify and store inventory up to 75 percent faster at fulfillment centers.
Meanwhile, DHL Supply Chain and Locus Robotics reached another useful measure of scale in 2026: one billion warehouse picks using Locus AMRs. Locus says thousands of its robots now operate across more than 40 DHL-managed sites worldwide. These examples are different applications with different economics. That is precisely the point. The warehouse automation market is moving beyond the question of whether robotics can work. Leading operators are increasingly confronting the harder questions of where automation should be deployed, how quickly it can scale, how well it integrates with existing operations, and whether benefits survive replication across a network.
The Metrics That Matter After Go-Live
The risk in covering a $6 billion automation agreement is treating announced spending as though it were demonstrated return. It is not. The more valuable story will develop as the systems go live. The measures worth watching include throughput, storage utilization, replenishment performance, labor productivity, system availability, fulfillment speed, implementation cost and the ability to maintain performance during demand peaks. That distinction should matter to technology buyers. A compelling demonstration can show what automation can do. A network-scale deployment begins to show whether the technology can generate similar value repeatedly under different facility and operating conditions. For Walmart, that makes the 25 distribution centers as important as the $6 billion headline.
Takeaway
The next chapter of warehouse automation will not be defined simply by more robots. It will be defined by whether operators can turn automation into a repeatable, measurable and scalable operating capability.
Walmart’s expanded relationship with Symbotic provides an unusually large test of that idea. The announced objectives are ambitious: more capacity, faster product movement, better replenishment, broader assortment, simpler work and lower costs. Now comes the more important part: measuring what changes when those systems are operating across the network. For other warehouse operators considering automation, that may ultimately be the most useful lesson from Walmart. Do not evaluate the robot alone. Evaluate what the automation changes in the economics and performance of the supply chain around it.
The post Walmart and Symbotic: When Warehouse Automation Becomes a Network Strategy appeared first on Logistics Viewpoints.


Octave Puts Trusted Industrial Data at the Center of OT Cybersecurity
The Systems-Engineered Logistics Operation: From Transformation Projects to Continuous Design
Walmart and Symbotic: When Warehouse Automation Becomes a Network Strategy
Freightos Global Freight Outlook – September 2026
Container rates jump another $1k/FEU – but is demand peaking? – July 8, 2026 Update

Walmart and the New Supply Chain Reality: AI, Automation, and Resilience
Trending
- Non classé2 mois ago
Freightos Global Freight Outlook – September 2026
- Non classé4 mois ago
Container rates jump another $1k/FEU – but is demand peaking? – July 8, 2026 Update
-
 Non classé2 ans ago
Walmart and the New Supply Chain Reality: AI, Automation, and Resilience
-
 Non classé7 mois ago
Why Sulfuric Acid Is Emerging as a Supply Chain Constraint in Copper
- Non classé5 mois ago
Container rates starting to spike on peak season rush – June 2, 2026 Update
- Non classé1 an ago
13 Books Logistics And Supply Chain Experts Need To Read
- Non classé1 an ago
Ex-Asia ocean rates climb on GRIs, despite slowing demand – October 22, 2025 Update
- Non classé4 mois ago
LCL Shipping Cost Calculator: Calculate Air and Sea Shipping Freight Rates