Non classé
Supply Chain and Logistic News March 3rd – 6th 2025

Published
2 ans agoon
By
Global supply chains are facing fresh disruptions as trade tensions escalate, digital innovation transforms logistics, and energy partnerships reshape infrastructure. The U.S. has imposed new tariffs on Canada, Mexico, and China, triggering retaliatory measures that could drive up costs and destabilize markets. Meanwhile, Hapag-Lloyd’s new Container Payment Portal streamlines cargo movement, and GE Vernova’s partnership with AWS accelerates energy transition efforts. BlackRock’s $19 billion acquisition of Panamanian ports underscores Wall Street’s growing influence in global trade, while Corning’s solar manufacturing alliance boosts U.S. energy independence. As businesses navigate these changes, resilience and strategic adaptation remain critical in an evolving economic landscape.
Here is the news for the week:
PayCargo and Gnosis Freight to Power Container Payment Portal for Hapag-Lloyd
The Container Payment Portal (CPP) is a new digital solution launched through a partnership between Hapag-Lloyd, PayCargo, and Gnosis Freight to enhance cargo movement efficiency across U.S. ports. The portal provides real-time container tracking, automated invoicing, seamless electronic payments, and integrated dispute resolution, ensuring compliance with the Ocean Shipping Reform Act of 2022 and recent Federal Maritime Commission regulations. By streamlining payment processing and container release, CPP reduces dwell times and improves transparency for Hapag-Lloyd customers and terminal operators. This phased rollout across major U.S. ports in 2025 underscores Hapag-Lloyd’s commitment to digital innovation in the shipping industry.
Trade War Ignites With US Implementing Tariffs on Closets Trading Partners
The latest wave of tariffs between the U.S., China, and Canada is escalating global trade tensions, with significant economic consequences. President Trump’s new tariffs impose a 25% levy on most Canadian and Mexican imports and raise duties on Chinese goods from 10% to 20%, prompting swift retaliation. Beijing is targeting U.S. agricultural exports with additional 10%-15% tariffs, while Canada is hitting back with immediate 25% tariffs on $20 billion worth of U.S. goods, with more to follow. These moves threaten to disrupt supply chains, increase costs for businesses and consumers, and fuel market volatility. As North American trade relations strain and U.S. farmers face further pressure, the broader impact of this tariff war remains uncertain, but one thing is clear: economic uncertainty is on the rise.
A one-month exemption for cars and trucks that comply with the U.S.-Mexico-Canada Agreement’s complex content rules, as Trump has outlined, would be a delay for Ford, GM and Stellantis. Trump also might eliminate the 10% tariff on Canadian energy imports, such as crude oil and gasoline, that comply with the USMCA rules of origin, a source familiar with the discussions said.
GE Vernova and AWS Sign Strategic Partnership to Support AWS Data Center Expansion
GE Vernova and AWS have signed a strategic framework agreement to support AWS’s data center expansion while advancing energy transition efforts, grid security, and decarbonization. GE Vernova will provide AWS with electrification solutions, including substation connectivity, renewable energy collaboration, and power generation services. In return, AWS will support GE Vernova’s cloud migration and digital innovation, including AI-driven solutions and high-performance computing. The partnership aims to enhance energy efficiency, optimize operations, and drive sustainability across both organizations while expanding cloud-based solutions for the energy sector.
Black Rock Signs 19 Billion Dollar Deal to Purchase Panama Canal
Through its infrastructure investment arm, BlackRock has agreed to buy two key Panamanian ports from Hong Kong-based CK Hutchison for $19 billion, easing tensions between Panama and President Trump, who falsely claimed China controlled the Panama Canal. The deal, backed by the Trump administration, provides an “off-ramp” from the political standoff and aligns with Trump’s America First policy, benefiting U.S. financial interests. CK Hutchison, under pressure, sought an American buyer, while BlackRock saw the acquisition as a strategic expansion in global infrastructure. Despite Panama’s official stance that the transaction is purely commercial, the move highlights Wall Street’s deep influence in Latin America.
Technology Company “Corning” Strikes Deal with US Solar Manufacturer Suniva and Heliene
This solar partnership will produce the only solar panels made with all American components. This alliance marks a major milestone in efforts to establish a U.S. solar manufacturing hub. Currently, the biggest solar manufacturer and user is China. Last year alone, China installed more solar capacity than the total amount ever installed in any other country. They currently have 40% of the world’s entire solar capacity, the United States comes in second with 12%. The company Heliene is based in Canada but produces panels in Minnesota. Corning and its subsidiary Hemlock Semiconductor produce silicon wafers and polysilicon, the solar industry’s raw material, in Michigan. The new modules contain a solar cell with up to 66% domestic content. This product would allow solar project developers to qualify for a bonus domestic content tax credit of 10% on top of the base IRA tax credit for clean projects of 30%.
Song of the week:
The post Supply Chain and Logistic News March 3rd – 6th 2025 appeared first on Logistics Viewpoints.
You may like
Non classé
OpenAI’s Pierre Acquisition Signals a New Era for Supply Chain Software Development
Published
1 heure agoon
5 novembre 2026By
One of the enduring lessons of supply chain management is that increasing throughput at one stage of a process does not necessarily improve performance across the entire operation. More production capacity has limited value if distribution cannot move the finished goods. A faster warehouse picking operation accomplishes little if packing and shipping cannot keep pace. The constraint simply moves. Artificial intelligence is now creating a similar problem in software development, and the implications for enterprise supply chain applications could be substantial.
On November 4, OpenAI announced its intention to acquire Pierre Computer Company, a developer of tools for navigating, reviewing, editing, and storing software code. The proposed acquisition follows OpenAI’s November 2 announcement of Pando, an internally developed source control backend designed to support the growing volume of parallel engineering work performed by developers and AI agents. Together, these announcements point to an important transition. Generating code is becoming faster and more accessible, but the surrounding processes for understanding, validating, integrating, and controlling that code must evolve at the same pace.
For transportation management, warehouse management, manufacturing, and supply chain planning software suppliers, this is more than a development productivity story. It has implications for how quickly vendors can modernize complex applications, how reliably they can introduce new functionality, and how enterprise customers should assess the risks associated with AI-assisted software engineering.
The Constraint Moves from Writing Code to Managing Change
Software engineering has traditionally been organized around the capacity of human development teams. Engineers implement changes, colleagues review them, automated tests check for defects, and approved modifications move through release processes. Development tools have become more sophisticated, but the flow of work has generally remained tied to the pace at which people can produce and assess changes.
Coding agents alter that relationship. A developer can assign several agents to investigate defects, update interfaces, create tests, or modify different parts of an application concurrently. The output may arrive faster than the organization can evaluate it. More proposed changes mean more competing branches, integration conflicts, regression testing, and decisions about what is safe to release.
Pierre’s technology addresses part of this growing challenge. Its Trees and Diffs libraries, already used in Codex, help developers navigate code and inspect changes. Its additional tools support editing, highlighting, and Git-based code storage. Pando addresses another part of the problem by scaling source control infrastructure for highly parallel activity. OpenAI’s stated ambition is to connect the code an organization ships with the decisions its people make.
These are complementary capabilities, not a complete solution to software assurance. Better code navigation and source control can make large volumes of changes easier to manage, but neither establishes that a modification is operationally correct. That distinction becomes particularly important in supply chain systems, where software behavior is tightly connected to physical operations and commercial obligations.
Why Supply Chain Applications Raise the Stakes
A transportation management system is not simply a collection of screens and workflows. It embodies carrier contracts, shipment constraints, service commitments, rating logic, routing rules, and integrations with customers and execution partners. A change that appears technically valid can still alter carrier selection or delivery promises in ways that are commercially significant.
Warehouse applications are similarly exposed. A modification to allocation logic, replenishment priorities, or exception handling may affect inventory availability and the sequence of work on the floor. The code may compile, automated tests may pass, and a user interface may look correct while a less visible operational assumption has changed. Supply chain planning platforms add further complexity through data models, optimization engines, scenarios, and dependencies across business functions.
This is why the value of AI-assisted development cannot be measured simply by the amount of code produced. The relevant issue is whether suppliers can translate faster engineering activity into dependable releases without introducing unacceptable operational risk.
There is meaningful upside. Many established supply chain platforms carry years of accumulated customization, aging interfaces, integration code, and technical debt. Coding agents could help suppliers document legacy systems, generate tests, modernize components, and accelerate repetitive maintenance. They may also make it more economical to address narrow customer requirements that previously competed for scarce engineering resources.
Yet the harder work often lies in understanding why existing behavior matters. An old exception rule may reflect a customer contract, a regulatory requirement, or a hard-won lesson from a previous implementation. Removing or refactoring that logic without understanding its business purpose can create problems that are not readily apparent from the code itself. Domain expertise and traceable requirements therefore become more valuable as automated development accelerates, not less.
The distinction is also important for enterprise buyers. An agent used by a software vendor to build or maintain an application is different from an operational agent authorized to make transportation or inventory decisions. Both require governance, but the controls are not interchangeable. The first must produce reliable software changes; the second must operate within defined business permissions and decision boundaries.
Development Traceability Becomes a Competitive Capability
OpenAI’s interest in connecting shipped code with human decisions points toward a broader challenge in enterprise engineering. When an agent proposes a change, the organization needs to retain the link between the original requirement, the agent’s instructions, the resulting modification, the tests performed, and the approval to release it. A conventional version history can show what changed, but it does not necessarily establish why the change was justified or whether it preserved the intended business outcome.
For supply chain software, that evidence matters across product upgrades, customer-specific extensions, cybersecurity reviews, and regulated environments. A supplier should be able to explain not only that a modification passed technical checks, but also how its effect on relevant business rules, interfaces, and operational scenarios was evaluated.
The acquisition does not mean Codex already supplies this full governance chain. OpenAI and Pierre will remain separate until the transaction closes, subject to customary conditions and regulatory approvals. OpenAI has said Pierre’s open-source projects will remain open source and that Code Storage customers can continue using the service after closing as functionality is brought into Codex. The broader ambition is clear, but the implementation and commercial impact remain to be demonstrated.
What can already be anticipated is a change in how software suppliers compete. AI-generated code may become increasingly accessible across the industry. Greater differentiation could come from engineering systems that combine speed with rigorous validation, architectural consistency, security, and controlled deployment. Suppliers that manage these disciplines effectively may be better positioned to maintain complex installed bases and deliver improvements without adding equivalent engineering overhead.
That should also change vendor due diligence. Enterprise buyers should look beyond claims about AI coding productivity and examine the time required to deliver validated functionality, escaped defects, rollback rates, compatibility with existing customer configurations, and the ability to reconstruct how changes were reviewed and approved. These measures are more meaningful than lines of code generated or the number of tasks completed by autonomous agents.
A Familiar Supply Chain Lesson Applied to Software
OpenAI’s proposed acquisition of Pierre is a relatively specialized event in the developer tools market, but it illustrates a development with broader consequences for enterprise technology. As coding agents increase the supply of software changes, review, integration, testing, and release management become potential constraints on the entire development process.
Supply chain leaders have seen this pattern before. Improving the performance of one operation creates limited value when the rest of the network cannot absorb the additional throughput. The solution is not simply more capacity at the original bottleneck; it is coordinated improvement across the system.
The same principle applies to AI-assisted engineering. Software vendors will not create lasting advantage merely by generating changes faster. They will do so by converting that speed into reliable product improvements, maintaining accountability for business logic, and protecting the operational continuity their customers depend on.
The significance of the Pierre announcement is therefore less about another acquisition in artificial intelligence and more about the changing economics of enterprise software development. The next competitive advantage may belong not to the company that produces the most code, but to the one that can validate, govern, and deploy useful changes with the greatest confidence.
The post OpenAI’s Pierre Acquisition Signals a New Era for Supply Chain Software Development appeared first on Logistics Viewpoints.
Non classé
Octave Puts Trusted Industrial Data at the Center of OT Cybersecurity
Published
16 heures agoon
4 novembre 2026By
Octave is revamping its cybersecurity and operational technology software portfolio with a broader platform strategy emphasizing trusted industrial data, operational resilience, and ecosystem integration. A key component of this strategy is Octave Cyber Integrity, which addresses the need for accurate, detailed, and continuously updated information regarding assets, configurations, vulnerabilities, and changes across diverse control system environments in the world of OT.
Octave is positioning Cyber Integrity as a reliable foundation for OT cybersecurity by integrating deep configuration-based asset identification with broader industrial data sources. This approach signifies an intensified commitment and acceleration of capabilities to provide the market with continuously maintained, accurate cybersecurity data, which is critical for operational resilience, risk prioritization, ecosystem collaboration, and AI-enabled decision-making.
Octave takes a different approach from traditional OT asset discovery models that mainly rely on passive network monitoring or active scanning. The company emphasizes configuration-based visibility using backups and control system data to create a comprehensive representation of industrial assets, including devices from Level 0 to Level 3.5, as well as firmware, software, I/O, control strategies, patch status, and configuration baselines. This method is well-suited for critical infrastructure environments where active interrogation of control assets could introduce operational risks.
Octave’s new platform direction means that cybersecurity data is now being integrated into the industrial data layer rather than existing as a separate security dataset. By providing access to Cyber Integrity data through an intelligent layer, and eventually through APIs for third-party security and other cybersecurity vendors, Octave is establishing asset integrity and data integrity as essential for AI-enabled operations, more effective cyber risk management, and collaborative OT cybersecurity initiatives. With this approach to data, the company is also laying the foundation for the creation of a cybersecurity digital twin.
Octave Is Reframing Industrial Software Around Trusted Data
Octave is an independent software and SaaS company that emerged from Hexagon’s planned separation of several software businesses, including Hexagon’s Asset Lifecycle Intelligence and Safety and Infrastructure & Geospatial divisions, along with ETQ, Bricsys, and Projectmates. Hexagon announced the Octave name in 2025 as the identity for the spin-off, and the company completed its separation in mid-2026. Octave now operates as a standalone public company (Nasdaq: OCTV) focused on mission-critical software for industrial and public-sector organizations.
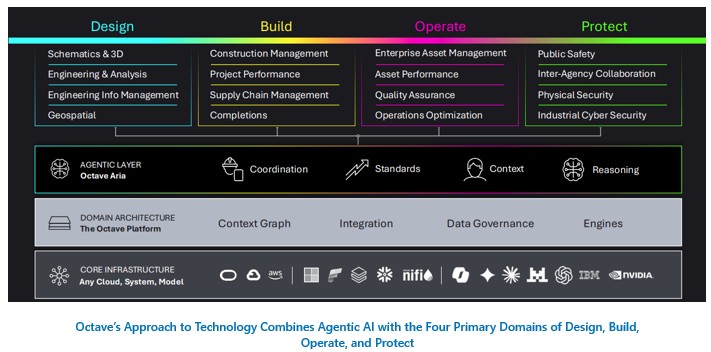
The company inherits a broad portfolio built around the lifecycle of physical assets. Its new approach spans four workflow environments: design, build, operate, and protect. This heritage means that Octave does not approach cybersecurity as a standalone discipline. It connects cybersecurity to engineering data, operations, asset lifecycle management, public safety, physical security, and quality workflows.
Octave positions itself as a differentiated industrial software company by combining engineering, operations, safety, cybersecurity, and physical security capabilities around an AI-ready industrial data fabric and continuous digital thread. Its strategy emphasizes open, contextualized data, SaaS delivery, and human-guided industrial AI to help asset-intensive organizations improve lifecycle efficiency, resilience, and operational decision-making.
Octave’s New Business Approach: A Common Foundation of Contextual Data
Octave’s new business approach moves the company beyond a product-centric model toward a platform and ecosystem model. Instead of treating OT cybersecurity, physical security, engineering data, and operational intelligence as isolated domains, Octave emphasizes a common foundation of contextualized industrial data. This approach aligns with the requirements of asset-intensive industries that must manage security, reliability, safety, compliance, and operational performance across complex multi-site operations.
This strategy matters most in industries such as oil and gas, power, chemicals, and utilities, where valuable cybersecurity insights often depend on engineering context and configuration detail that traditional IT security tools do not capture. Octave recognizes that no single vendor or detection method can fully address OT cybersecurity on its own. Effective programs require accurate asset intelligence, configuration integrity, operational context, and mechanisms to share trusted data with adjacent tools and workflows.
The Octave Platform: Building an Industrial Data Layer
The Octave platform strategy centers on a unified, trusted data layer that supports design, build, operate, and protect workflows. Cybersecurity data, especially asset inventory and configuration information, becomes a key input to this intelligence layer. In this model, OT cybersecurity extends beyond threat detection. It also requires a reliable representation of the industrial environment so security, operations, and engineering teams can act from a shared source of truth.
This platform direction matters because many OT risk programs still operate with fragmented asset data. Passive discovery tools identify network-connected devices, vulnerability tools maintain separate patch records, engineering systems hold configuration data, and compliance teams track controls in separate processes. Octave seeks to consolidate these data domains so organizations can use asset identity, configuration state, vulnerability exposure, backup status, and operational context together for faster and more effective remediation and mitigation of OT cybersecurity risk.
Octave Cyber Integrity and the Role of Deep Asset Identification
Cyber Integrity sits within Octave’s Protect portfolio. The product has its roots in PAS Cyber Integrity, which Hexagon previously offered through its Asset Lifecycle Intelligence business. As part of Octave, Cyber Integrity can now support a solution-level approach that combines deep OT asset and configuration data with lifecycle intelligence, operational context, and domain-specific AI. Octave Cyber Integrity identifies, evaluates, and prioritizes OT/ICS cybersecurity risk by capturing critical asset, vulnerability, and configuration data. This elevates the role of Cyber Integrity to that of a risk management and resilience platform for multi-vendor industrial control system environments.
Octave’s value proposition depends on the distinction between basic asset discovery and deep asset identification. Passive IDS-based discovery provides useful network visibility, including IP addresses, MAC addresses, and traffic relationships. However, passive discovery alone often lacks the depth required to validate control system configurations, identify firmware and software detail, understand patch posture, or maintain a known-good baseline. Active scanning adds detail, but in sensitive OT environments it can raise concerns about device stability, vendor warranty exposure, and operational disruption.
Cyber Integrity addresses this gap with a configuration-based approach. It collects backups and control system configuration data to build a more detailed inventory without directly interrogating live control assets in ways that could affect operations. This method requires more time and engineering effort than passive packet capture, but it provides richer data for vulnerability assessment, configuration change detection, compliance, recovery, and lifecycle planning.
Asset Integrity, Data Integrity, and OT Cybersecurity
Cyber Integrity links asset identification with data integrity by establishing a trusted representation of what exists in the control environment, how each asset is configured, whether that configuration has changed, and how those changes affect cyber risk and operational resilience. In OT environments, inaccurate data can lead to missed vulnerabilities, poor remediation priorities, failed audits, delayed recovery, and unnecessary operational disruption.
Deep configuration data also improves vulnerability management. Rather than relying only on generic device identification or network observations, organizations can correlate asset attributes, patch levels, firmware, installed software, system criticality, and configuration state. This context gives teams a stronger basis for determining whether a vulnerability applies, whether remediation is technically feasible, and which actions deserve priority based on operational impact.
Data integrity becomes all-important as industrial organizations apply AI and advanced analytics to OT cybersecurity and operations. AI models depend on the quality, completeness, and trustworthiness of the data they consume. By feeding verified asset and configuration data into a common intelligent layer, Octave positions Cyber Integrity as an enabler of more reliable analytics, decision support, threat detection, and remediation workflows.
Ecosystem and API Strategy
Octave also plans to expose deep asset inventory data through APIs for integration with third party cybersecurity vendors. Most end users rely on multiple tools, including passive monitoring, threat detection, vulnerability management, SIEM, and service management platforms. No single vendor owns the full workflow. By opening Cyber Integrity data to partners, Octave can allow products from vendors such as Dragos, Nozomi Networks, and Claroty to use a deeper asset and configuration foundation, subject to partner agreements and customer approvals. This approach strengthens the broader OT cybersecurity ecosystem by improving data quality across detection, vulnerability prioritization, incident response, and compliance workflows.
Recent Attacks on US Water Infrastructure Show the Importance of Good OT Asset and Configuration Data
Recent attacks on U.S. water and wastewater infrastructure underscore why trusted OT asset and configuration data have become operationally critical. Federal agencies have warned that malicious actors are targeting internet-facing programmable logic controllers, including Rockwell Automation/Allen-Bradley MicroLogix controllers, changing IP addresses and passwords, modifying project files, and causing operational effects such as loss of monitoring, loss of control, pressure loss, flooding, boil-water notices, and sustained manual operations. Earlier campaigns against PLCs in the water sector showed a similar pattern: exposed control devices, weak or default credentials, and limited visibility into controller configurations created opportunities for attackers to disrupt or deface operational systems.
Octave Cyber Integrity is relevant to these incidents because it focuses on the underlying weaknesses that made them possible. Incomplete OT inventories, undocumented internet exposure, weak configuration control, and limited ability to compare current controller state with trusted baselines are all major contributors to the likelihood of a serious cyber incident. By maintaining detailed asset identity, firmware, software, configuration, backup, vulnerability, and change data, Cyber Integrity can help water utilities identify exposed or misconfigured PLCs, validate whether unauthorized changes have occurred, prioritize remediation based on operational criticality, and restore systems from known-good backups. In this context, Cyber Integrity becomes more than an inventory exercise; it becomes a practical foundation for resilience in water infrastructure where operators must preserve safe service even when control systems are targeted.
Creating a Cybersecurity Digital Twin
Cyber Integrity data and the Octave platform have the potential to combine to create a cybersecurity digital twin. In this model, Cyber Integrity would provide the detailed technical foundation: asset identity, firmware, software, configuration files, control logic, backup status, patch levels, vulnerability exposure, and change history. The Octave platform would add lifecycle context, operational relationships, engineering data, workflow status, and domain-specific intelligence. Together, these data sets could create a continuously maintained digital representation of the OT cyber-physical environment.
Cybersecurity digital twins differ from traditional engineering digital twins because they focus on cyber risk, configuration integrity, and operational resilience. A cybersecurity digital twin can show which assets exist, how they connect to processes and systems, what known-good configurations look like, where vulnerabilities apply, which changes deviate from approved baselines, and how a cyber event or remediation action could affect operations. Security, engineering, and operations teams could use this shared model to evaluate cyber risk before taking action in the live environment.
The concept could also improve incident response and recovery. If an organization maintains a current cyber twin, it can compare the live environment with trusted baselines, identify unauthorized changes, assess the operational importance of affected assets, and prioritize restoration from validated backups. This would move cyber recovery from a largely reactive process toward a more structured, model-driven workflow that links cybersecurity decisions to process criticality and asset lifecycle data.
Over time, a cybersecurity digital twin could become a foundation for AI-assisted risk analysis. Octave could use verified Cyber Integrity data and broader platform context to help teams simulate attack paths, evaluate remediation options, identify high-risk configuration drift, and recommend actions based on both cyber exposure and operational impact. The value of this model would depend on data quality, governance, integration with partner tools, and the customer’s ability to keep the twin synchronized with the real OT environment.
Conclusions & Recommendations
Octave’s approach reflects an important industry trend: effective OT cybersecurity increasingly depends on the integrity of the underlying industrial data. Cyber Integrity is more than a simple OT asset inventory product. It serves as a source of trusted industrial cybersecurity data that supports risk management, resilience, compliance, and AI-enabled decision-making across the broader Octave platform. By capturing backups and configuration data, Cyber Integrity helps organizations build a more complete understanding of assets, vulnerabilities, baselines, and unauthorized change. Octave’s planned API and ecosystem strategy could further increase the value of Cyber Integrity by allowing customers and partner tools to use deep asset data without duplicating collection efforts. In ARC’s view, Octave is well positioned to benefit from growing market demand for reliable OT asset intelligence and stronger integration between cybersecurity, operations, and engineering data.
End users should evaluate Octave’s approach against their OT cybersecurity maturity. Early-stage programs may begin with passive discovery to establish basic visibility. More mature programs, especially in critical infrastructure, will benefit from using deep configuration-based inventory to strengthen vulnerability management, change control, compliance, backup, recovery, and operational resilience.
Octave’s platform strategy also reinforces the need to treat OT cybersecurity as part of enterprise industrial data management. Asset inventory, configuration state, vulnerability posture, and recovery data should not remain isolated within specialized security tools. These data sets should inform engineering workflows, maintenance planning, modernization decisions, compliance reporting, and executive-level cyber risk governance.
The post Octave Puts Trusted Industrial Data at the Center of OT Cybersecurity appeared first on Logistics Viewpoints.
Non classé
The Systems-Engineered Logistics Operation: From Transformation Projects to Continuous Design
Published
2 jours agoon
3 novembre 2026By
For years, logistics transformation has been organized as a succession of projects. Implement the platform. Build the control tower. Automate the facility. Add the AI layer. The problem is that logistics no longer changes on a project cadence.
That environment is disappearing. The future logistics will need to be designed continuously. The Autonomous Logistics Network is one expression of this end state, but reaching it requires continuous design rather than a one-time transformation project.
Stop Thinking in Technology Stacks
Modern logistics networks are becoming integrated combinations of physical assets, software, data, optimization, AI, robotics, people, partners, and automated decisions. Calling this a technology stack understates what is happening.
It is an operating system. The important design questions are no longer confined to which applications a company owns. Leaders have to consider how decisions flow, how data maintain continuity across systems, how automation interacts with people, how models are governed, how exceptions escalate, and how the organization behaves when components fail.
That is systems engineering territory. The companies that manage this architecture deliberately will have an advantage over those that continue adding capabilities one project at a time.
Intelligence Is Moving to the Point of Action
Logistics technology is moving from systems of record toward systems of decision. Traditional applications captured transactions and supported workflows. Analytical systems added prediction and optimization. The emerging layer increasingly combines real-time signals, AI, optimization, agents, and execution connectivity.
The result is intelligence closer to the point of action. A shipment delay can be identified, its impact evaluated, alternatives generated, and a response executed with limited human intervention. Transportation systems can continuously re-evaluate routes, capacity, and exceptions instead of waiting for manual replanning. Warehouse and yard systems can adjust priorities as conditions change.
This will make logistics faster. It will also make architecture and governance more consequential.
When software only reported information, a bad output could be ignored. When software acts, the operating envelope matters.
Human Work Moves Up the Decision Stack
More automation does not eliminate the human role. It changes it.
People will spend less time collecting information, reconciling spreadsheets, monitoring routine transactions, and making repetitive bounded decisions. They will spend more time dealing with novel exceptions, cross-functional tradeoffs, strategic choices, carrier and customer relationships, system design, and governance.
That is a better use of human capability. It is also a harder job.
The future planner, transportation manager, warehouse leader, or logistics executive will need to understand not only operations but the automated systems influencing operations. They will need to know when to trust a recommendation, when to challenge it, and how a decision in one part of the system affects another. Logistics expertise will become more architectural.
Continuous Design Requires Continuous Validation
If the system changes continuously, validation must become continuous as well.
AI models drift. Business priorities change. automation rules evolve. New interfaces are added. Local process changes accumulate. External conditions move.
The organization cannot wait for the next transformation program to determine whether the operating system still meets its requirements. Performance, model behavior, exception patterns, overrides, decision latency, data quality, and failure modes will need ongoing monitoring.
This creates a closed lifecycle: design, deploy, observe, validate, improve, and redesign. Transformation becomes less of an event and more of a management discipline.
Resilience Becomes an Architectural Property
The future of resilience is also likely to move beyond static buffers. Inventory and redundancy will remain important, but digital systems will make logistics more capable of sensing, simulating, and responding dynamically.
A disruption can trigger scenario analysis. A digital twin can estimate consequences. Optimization can evaluate alternatives. AI can interpret unstructured signals. Automated decision systems can act inside approved boundaries.
This does not eliminate the need for physical resilience. It allows physical resilience and decision resilience to work together.
The strongest logistics networks will not simply carry more protection. They will understand their dependencies and reconfigure faster when conditions change.
Architecture Becomes a Competitive Capability
For years, companies differentiated logistics through network scale, facility and transportation assets, carrier leverage, operational excellence, service design, and technology investment. Architecture is becoming another source of advantage.
Two companies may use similar software and still achieve very different results because one has better process integration, clearer decision rights, stronger data, more effective automation boundaries, better failure recovery, and tighter governance. The advantage does not come from owning the component. It comes from how the components have been engineered to work together.
Logistics Management Becomes Systems Management
That may be the larger lesson of this series. Logistics networks are already systems of systems. The technology is making them more connected, more autonomous, and more adaptive. That complexity cannot be managed indefinitely through functional optimization and periodic implementation projects.
The discipline has to evolve.
Define requirements before selecting solutions. Design the operating model. Architect processes, data, and decisions together. Engineer technology into the system rather than around it. Validate the outcome. Govern change. Design for failure. Improve continuously.
The competitive advantage will not come from owning the same AI, automation, TMS, WMS, visibility, and execution technologies everybody else can buy. It will come from how coherently those components have been engineered to work together. The future of logistics management is not simply more digital, more autonomous, or more intelligent. It is more engineered.
Related Logistics Viewpoints research
Systems Engineering in Logistics
The New Architecture of Logistics
2026 Supply Chain Decision Intelligence Market Map
Digital Transformation in Logistics
Previous in this series: Design for Failure: Resilience, Risk, and Failure Modes
Request the Systems Engineering in Logistics Client Edition
If your organization is evaluating a logistics transformation, technology strategy, automation program, or operating-model redesign, I would be glad to provide the complete client edition and discuss how the framework applies to your priorities, constraints, and operating environment.
The post The Systems-Engineered Logistics Operation: From Transformation Projects to Continuous Design appeared first on Logistics Viewpoints.

OpenAI’s Pierre Acquisition Signals a New Era for Supply Chain Software Development

Octave Puts Trusted Industrial Data at the Center of OT Cybersecurity
The Systems-Engineered Logistics Operation: From Transformation Projects to Continuous Design
Freightos Global Freight Outlook – September 2026
Container rates jump another $1k/FEU – but is demand peaking? – July 8, 2026 Update

Walmart and the New Supply Chain Reality: AI, Automation, and Resilience
Trending
- Non classé2 mois ago
Freightos Global Freight Outlook – September 2026
- Non classé4 mois ago
Container rates jump another $1k/FEU – but is demand peaking? – July 8, 2026 Update
-
 Non classé2 ans ago
Walmart and the New Supply Chain Reality: AI, Automation, and Resilience
-
 Non classé7 mois ago
Why Sulfuric Acid Is Emerging as a Supply Chain Constraint in Copper
- Non classé5 mois ago
Container rates starting to spike on peak season rush – June 2, 2026 Update
- Non classé1 an ago
13 Books Logistics And Supply Chain Experts Need To Read
- Non classé1 an ago
Ex-Asia ocean rates climb on GRIs, despite slowing demand – October 22, 2025 Update
- Non classé4 mois ago
LCL Shipping Cost Calculator: Calculate Air and Sea Shipping Freight Rates